The $35K Performance Problem

The $35K Performance Problem

A Fortune 500 client was about to spend $35,000 on new hardware. Their Splunk searches were taking 2+ minutes, dashboards were timing out, and users were complaining daily. I found the real problem in 10 minutes. It cost $0 to fix.

Read Article
The Permission Problem

The Permission Problem

"Can you check why this search isn't working?" I looked at the query. Perfect syntax. Correct index. Should work. But it returned zero results. The problem? Permissions. The #1 invisible issue in enterprise Splunk.

Read Article
The Compliance Gap Nobody Monitors

Your Next Compliance Audit Doesn't Have to Start With a Spreadsheet

Every quarter, someone on your team spends days pulling CIS Benchmark scan data into spreadsheets just to answer one question: are we compliant? If you're already running CIS-CAT Pro scans and already running Splunk, that pipeline shouldn't require manual work.

Read Article
The STIG Checklist That Never Gets Done

Your STIG Checklist Results Deserve Better Than a Spreadsheet

Every quarter, someone on your team spends days pulling STIG checklist results into spreadsheets just to answer one question: are we compliant? CKL and CKLB files belong in your SIEM, not in a spreadsheet.

Read Article
Database Audit Logs: The 30-Day Challenge

Database Audit Logs: The 30-Day Challenge

"We need MSSQL audit logs in Splunk. How long will it take?" "30 days." The client looked shocked. Here's what most people don't understand about database log onboarding — and why rushing it causes production outages.

Read Article
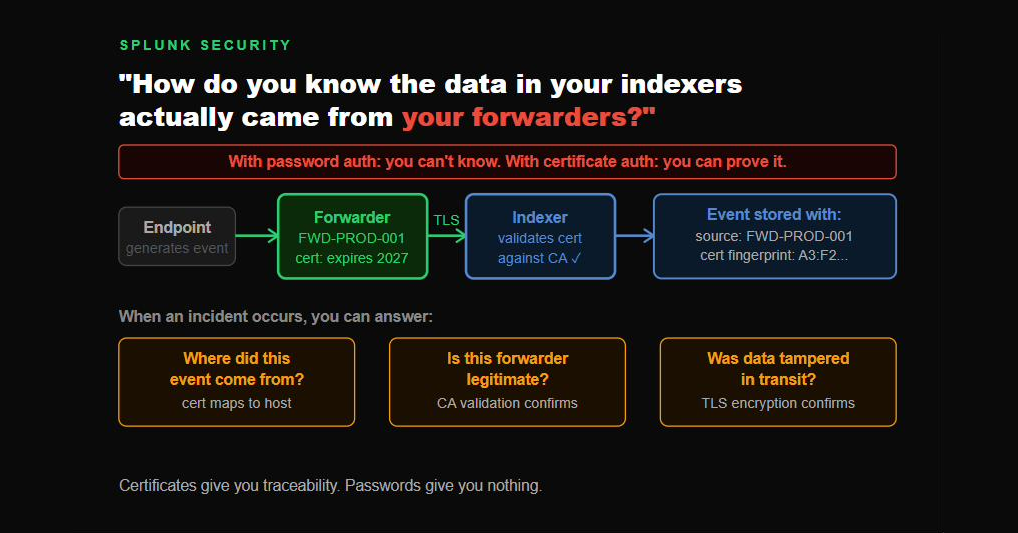
Certificate-Based Authentication for Splunk Forwarders — Enforcing Security for Data in Transit

Certificate-Based Authentication for Splunk Forwarders — Enforcing Security for Data in Transit

An auditor asked me a simple question during a STIG review. "How do you know the data coming into your Splunk indexers is actually from your forwarders?" The room went quiet. They were using username and password authentication.

Read Article
Storage Architecture: When Bucket Strategy Goes Bad

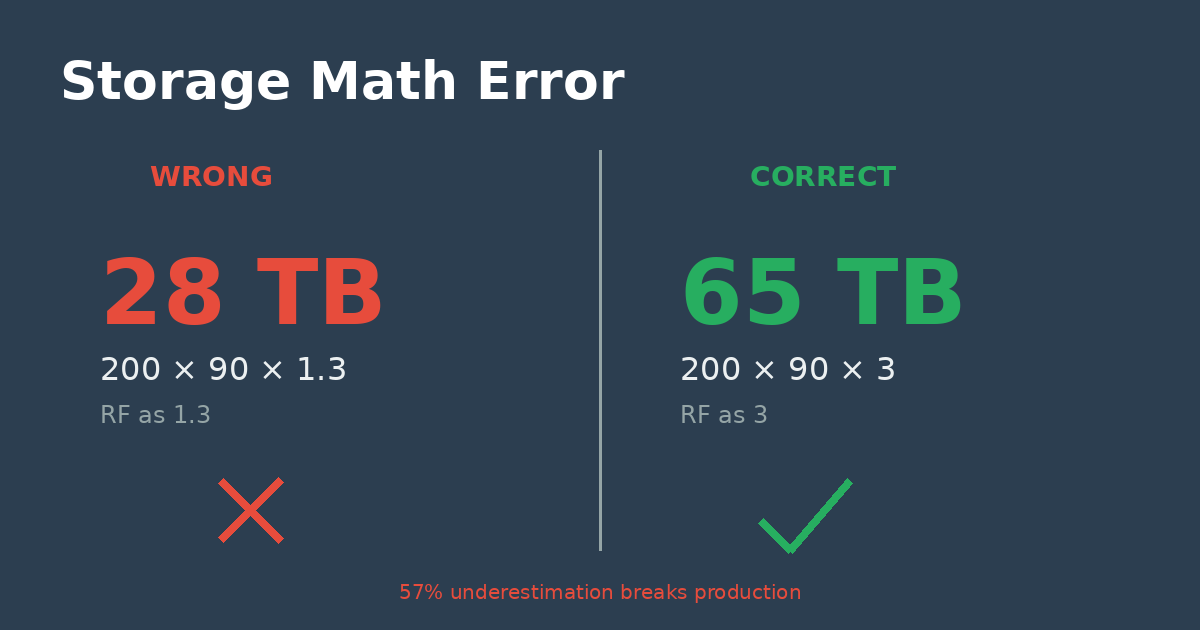
Storage Architecture: When Bucket Strategy Goes Bad

"Why is our hot storage at 95% capacity?" I looked at their Splunk environment. 30 TB of storage across the cluster. Plenty of space.

Read Article
The STIG Compliance Trap

The STIG Compliance Trap

The STIG checklist said "set minimum free disk space to 50%." So they did. And broke their entire Splunk environment. STIG compliance in Splunk isn't about following the checklist blindly.

Read Article
Environment Building Best Practices

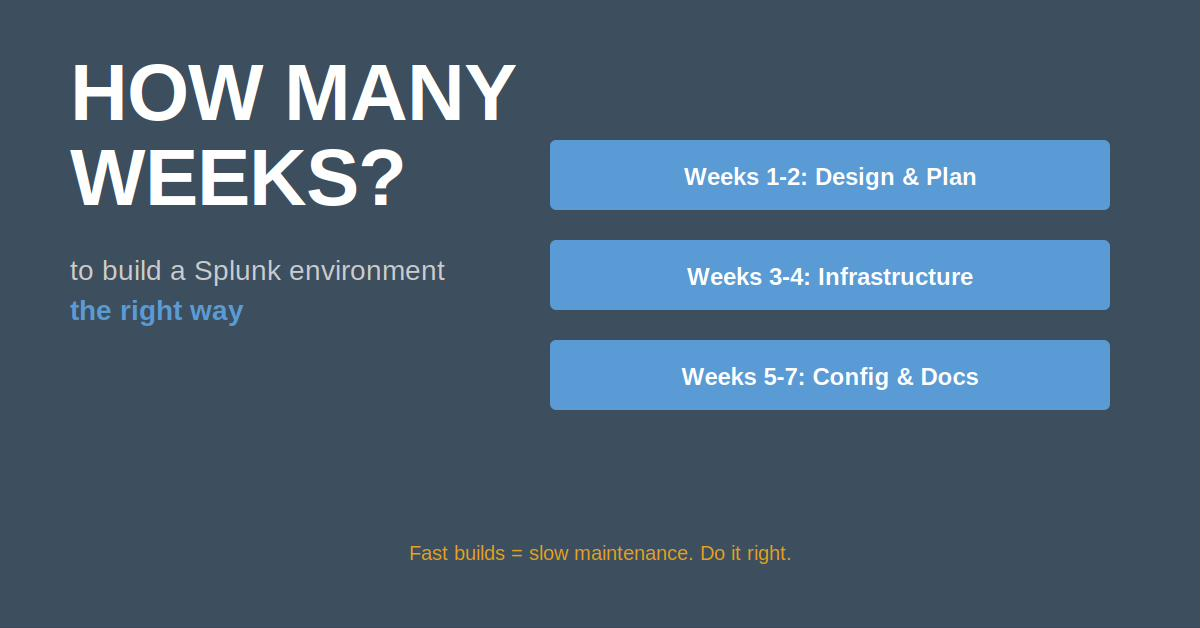
Environment Building Best Practices

"We're building a new Splunk environment. What's the fastest way to get it done?" Wrong question. The fastest way to build a Splunk environment is the slowest way to maintain one.

Read Article
Proactive Monitoring — Detecting Log Stoppage Before Users Report It

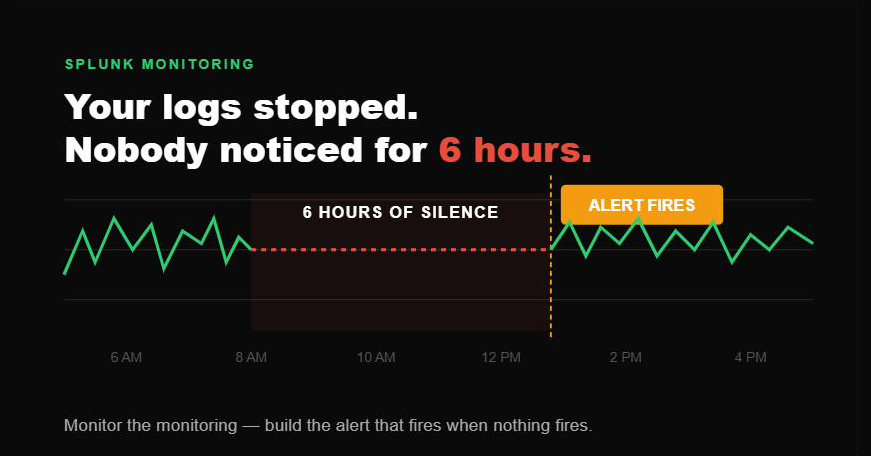
Proactive Monitoring — Detecting Log Stoppage Before Users Report It

The call came in at 2 PM on a Tuesday. "Marcus, our security dashboard hasn't updated since this morning. Are we under attack?" We weren't under attack.

Read Article
Forwarder Placement Strategy — Why Network Topology Decisions Matter

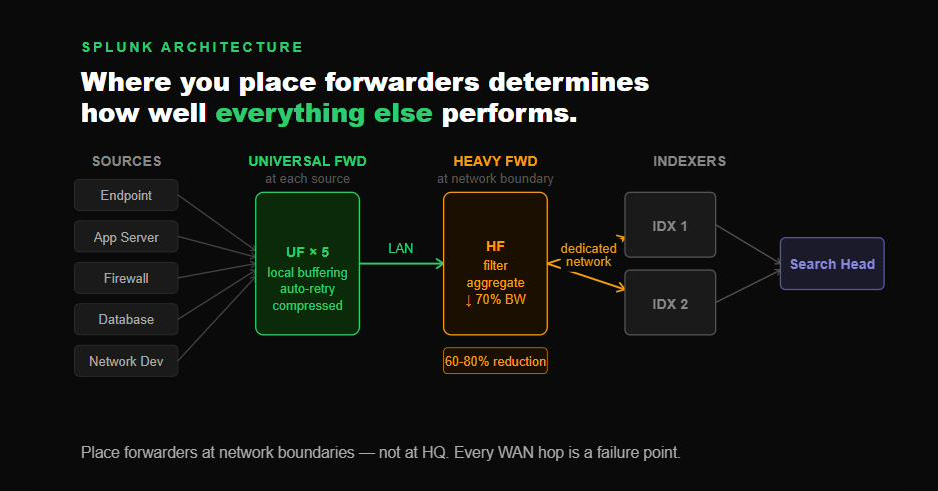
Forwarder Placement Strategy — Why Network Topology Decisions Matter

A client called me after their Splunk deployment went live. "Search performance is terrible. We bought the right hardware.

Read Article
Component Search: Find Any Vulnerable Component Across Your Entire Portfolio in 60 Seconds

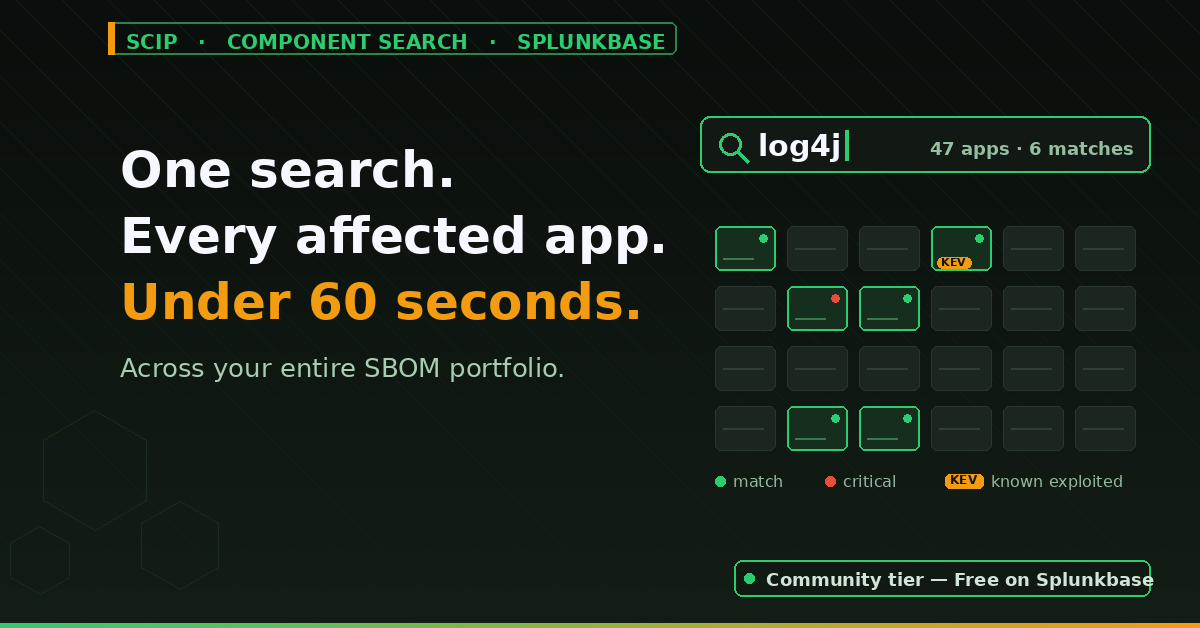
Component Search: Find Any Vulnerable Component Across Your Entire Portfolio in 60 Seconds

A new CVE drops. Critical severity. It affects a popular open-source library your development teams probably use.

Read Article
AI-BOM: The Model Inventory Your AI Systems Are Missing

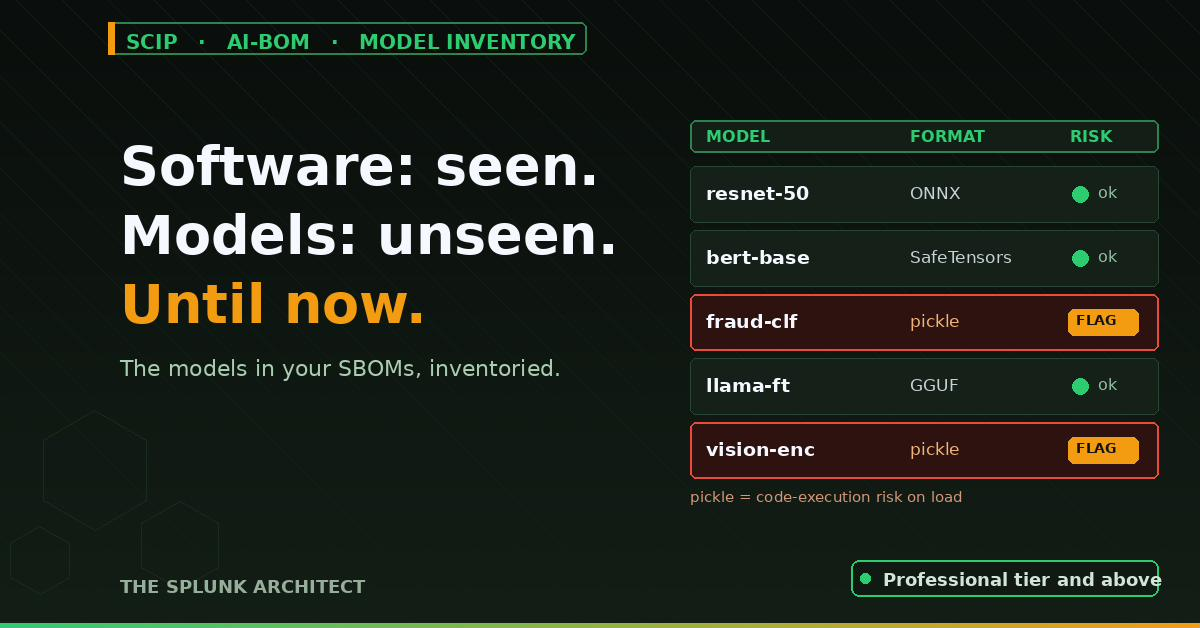
AI-BOM: The Model Inventory Your AI Systems Are Missing

For a decade, "know what's in your software" has meant the SBOM: components, versions, licenses, vulnerabilities. AI systems broke that model, literally. The most consequential thing in an AI system is often the model, and the model is not an ordinary software component.

Read Article
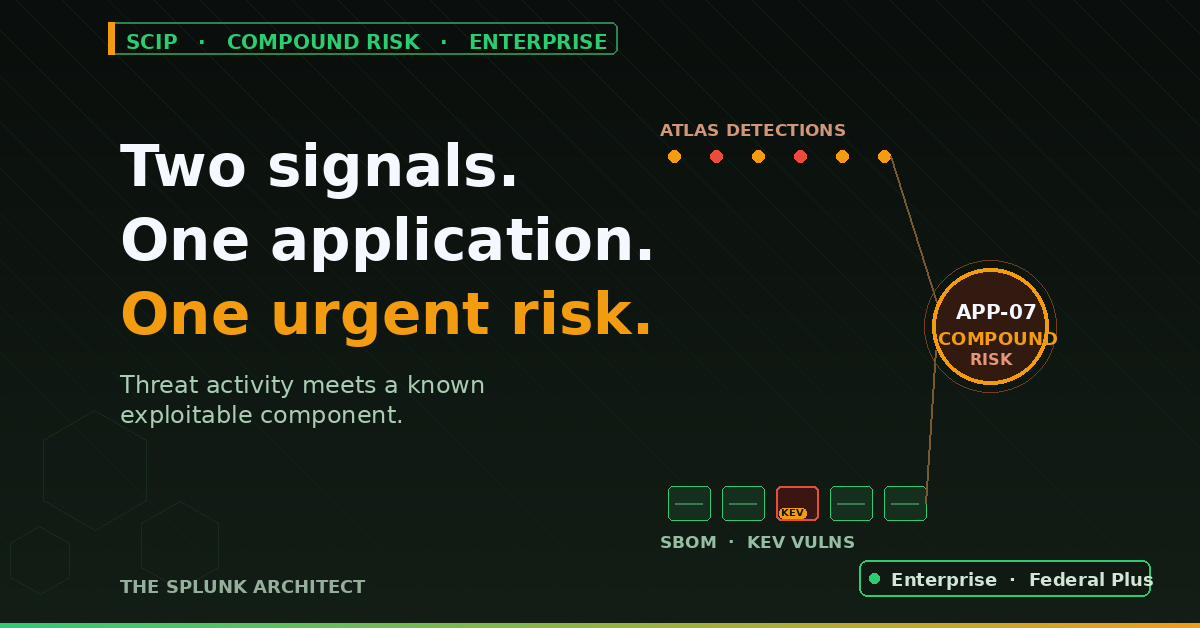
Compound Risk: The Threat Neither Dashboard Shows You Alone

Compound Risk: The Threat Neither Dashboard Shows You Alone

Most security programs watch threats against AI and software vulnerabilities as two separate disciplines, on two separate screens, owned by two separate instincts. That separation is reasonable. It is also where compound risk hides.

Read Article
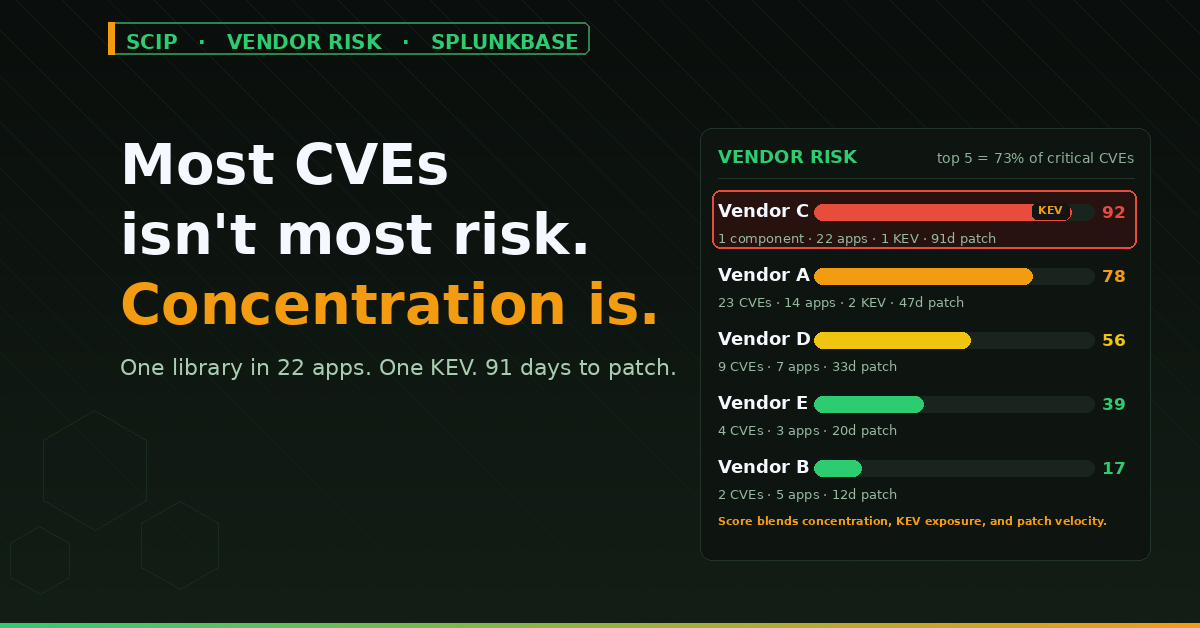
Vendor Risk: Which Third-Party Vendors Are Actually Killing Your Supply Chain Risk Score

Vendor Risk: Which Third-Party Vendors Are Actually Killing Your Supply Chain Risk Score

Your security team reports a supply chain risk score. Your board nods. Nobody asks the follow-up question: "Which vendor is driving that number?" When one vendor's components carry the highest risk score across your portfolio, that's not a vulnerability problem, it's a...

Read Article
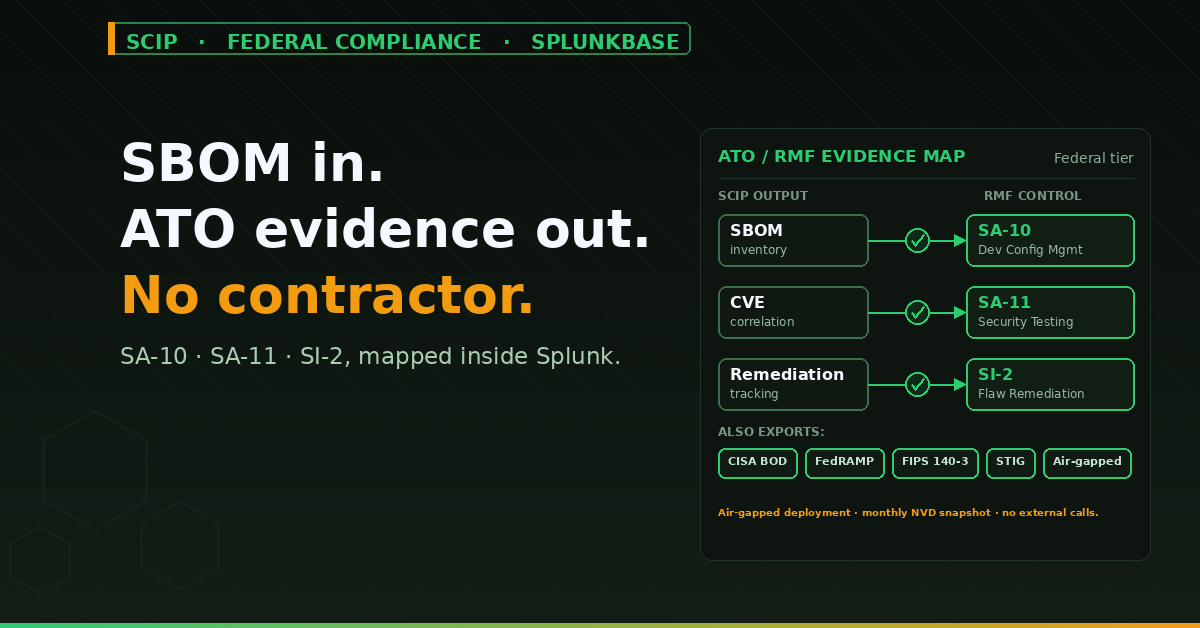
Federal Compliance Exports: Why Your ATO/RMF Team Needs Supply Chain Visibility Inside Splunk

Federal Compliance Exports: Why Your ATO/RMF Team Needs Supply Chain Visibility Inside Splunk

Your ATO package is due. The ISSO needs supply chain risk documentation mapped to SA-10, SA-11, and SI-2. Your development team has SBOMs somewhere, maybe.

Read Article
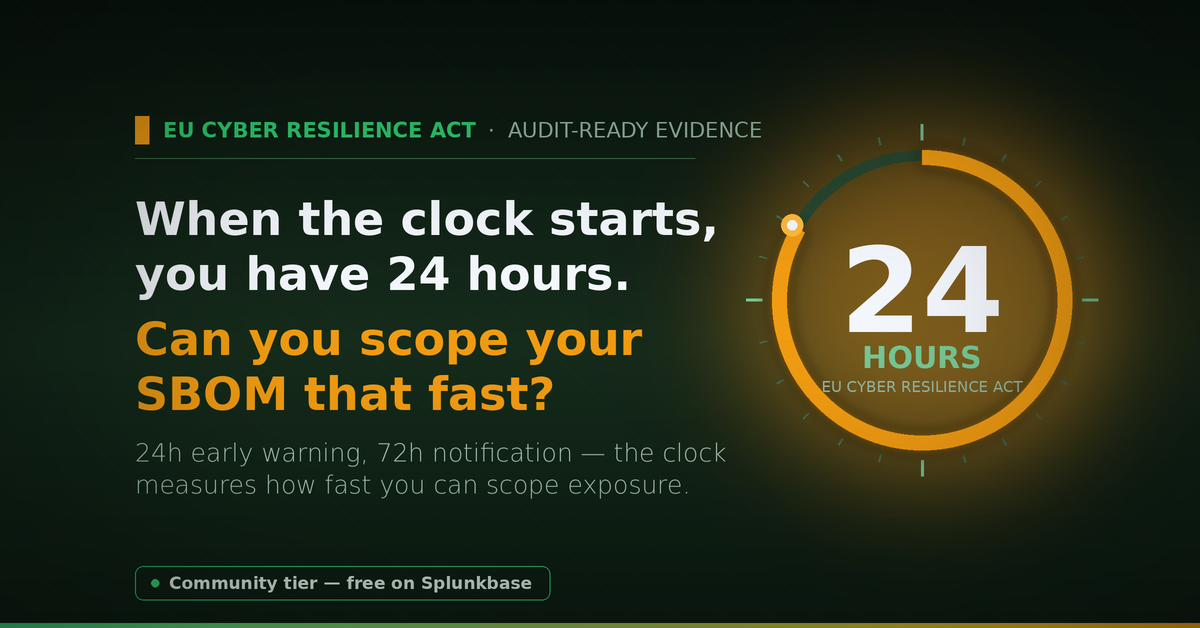
When the EU Cyber Resilience Act Clock Starts, You Have 24 Hours. Can You Scope Your SBOM That Fast?

When the EU Cyber Resilience Act Clock Starts, You Have 24 Hours. Can You Scope Your SBOM That Fast?

On September 11, 2026, a new clock starts for manufacturers of products with digital elements on the EU market. When an actively exploited vulnerability affects one of your products, you have 24 hours to file an early warning and 72 hours for a full notification, filed once...

Read Article
A Package You Trust Just Turned Malicious. Which of Your Builds Pulled It In?

A Package You Trust Just Turned Malicious. Which of Your Builds Pulled It In?

The xz-utils backdoor (CVE-2024-3094) was not a vulnerability in the ordinary sense. The code wasn't buggy. It was sabotaged, a maintainer-level compromise that planted a backdoor into a compression library sitting deep in the Linux dependency graph.

Read Article
The End of PDF Compliance: Federal Agencies Now Want Raw SBOM Data, Not a Signed Attestation

The End of PDF Compliance: Federal Agencies Now Want Raw SBOM Data, Not a Signed Attestation

For years, federal software compliance had a comfortable shape: produce a document, sign an attestation, submit a PDF. The artifact was the proof. That era is closing, on two fronts, for two different reasons.

Read Article
Which Meter Is Running? Reading a Splunk Bill Before You Try to Cut It

Which Meter Is Running? Reading a Splunk Bill Before You Try to Cut It

Every Splunk administrator has been handed the same assignment. The bill went up, nobody is quite sure why, and someone upstairs would like it to go down. What usually follows is a round of advice — filter at the edge, tune your retention, clean up your sourcetypes.

Read Article
Your SBOM's License Data Just Became a Legal Liability, Not a Footnote

Your SBOM's License Data Just Became a Legal Liability, Not a Footnote

Most teams treat the license column of an SBOM as paperwork, a field the tool fills in, that nobody reads. Two things are changing that. The EU Cyber Resilience Act puts security-and-support obligations on the products you place on the market, and CISA's finalized 2026...

Read Article